Treat any precise location tied to a mobile device as potentially sensitive data, verify the consent chain behind every location dataset you buy, and document supplier assessments before a campaign launches. The FTC’s action against Kochava and state statutes like the Colorado Privacy Act now hold buyers, not just brokers, accountable. Pause any unverified location data purchases and start a supplier review today.
TL;DR:
- Vendors must provide clear proof of where and how affirmative consent was obtained for location data use to meet current legal standards.
- Geolocation data that can identify visits to sensitive locations like clinics or places of worship increases regulatory risk, especially when linked to persistent device identifiers.
- Supplier assessments should include verification of consent records, exclusion of sensitive location categories, and enforceable deletion policies to reduce compliance exposure.
- Out-of-home campaigns relying on device-level location data should shift to first-party methods like QR codes or in-store interactions to minimize privacy risks.
- Maintaining detailed records of data collection, consent, and deletion efforts is essential for defending against regulatory or audit investigations.
Table of Contents
- Quick compliance checklist for the next 72 hours
- Which U.S. laws and enforcement actions matter for OOH campaigns
- Sensitive locations, precise geolocation, and regulatory risk
- Vendor due diligence: what to require in assessments and contracts
- Privacy-preserving measurement and first-party alternatives
- Consent, opt-outs, and consumer-facing execution for OOH
- Recordkeeping and incident response for OOH campaigns
- How Beacon Mobile Media maps OOH execution to privacy controls
- Data retention and deletion policies specific to OOH data
- Employee training and internal compliance programs for OOH privacy
- Handling consumer data subject access requests (DSARs) in OOH context
- International privacy regulations affecting OOH campaigns
- What this means for OOH teams right now
- Beacon Mobile Media: privacy-conscious OOH execution
- Sources
- FAQ
Quick compliance checklist for the next 72 hours
Marketing teams do not need a legal department to reduce exposure immediately. A few concrete moves close most of the near-term gap between what your campaign does and what regulators now expect.
- Pause purchases of precise location datasets that lack verifiable consent records tied to the original collection point.
- Run a supplier assessment before onboarding any location or measurement vendor, and get contractual representations on consent and deletion in writing.
- Classify whether your targeting or attribution data could reveal visits to a sensitive location, such as a clinic or place of worship.
- Document your campaign’s data purposes, retention windows, and opt-out channels in plain language before launch.
Pro Tip: Ask every location-data vendor for a written answer to one question: “Where did affirmative consent for this specific use occur?” If they cannot point to a moment and a mechanism, treat the data as unverified.
Which U.S. laws and enforcement actions matter for OOH campaigns
Out-of-home advertising used to sit outside most privacy conversations. Digital targeting and device-level measurement changed that, and enforcement has followed the data rather than the medium.
The FTC’s settlement with Kochava bans the company from selling sensitive location data without affirmative express consent and requires a sensitive-location program, supplier assessments, and deletion schedules. A similar FTC action against Mobilewalla required deletion routines and limits on reusing auction-derived location data, which matters directly for programmatic OOH buys that run through ad exchanges.
- The California Consumer Privacy Act defines precise geolocation and requires disclosure of data categories, honoring opt-out signals, and offering consumer request methods including DROP.
- The Colorado Privacy Act requires affirmative consent before processing sensitive data, including geolocation that could reveal health status or religious practice, and mandates data protection assessments for high-risk processing.
The practical takeaway: targeting logic, attribution reports, and vendor contracts all need to reflect these duties, not just your public privacy policy.
Sensitive locations, precise geolocation, and regulatory risk
California law treats geolocation as precise when it can identify a device’s location within a defined radius, a threshold set out in the CCPA statute. Regulators consistently flag certain location categories as sensitive regardless of the underlying law: medical facilities, reproductive health clinics, places of worship, shelters, and addiction treatment centers. Device-level datasets can reveal visits to these places even when a vendor calls the output “aggregated,” because small geofences around a single building rarely anonymize a handful of daily visitors.
Before using any location dataset, run this quick test:
- Ask whether the data is tied to a persistent device identifier rather than a household or zip code.
- Check whether any geofence in the dataset overlaps a sensitive-location category.
- Confirm whether the vendor can produce a consent record for the specific use, not just a general privacy policy reference.
- Determine whether deletion happens on a defined schedule or only on request.
A dataset that fails any of these checks carries meaningfully higher regulatory risk, even if it technically meets a vendor’s own internal privacy standard.
Vendor due diligence: what to require in assessments and contracts
Physical OOH cannot show a consent banner on a billboard, so compliance depends almost entirely on what happens upstream with your data and measurement suppliers. Practitioner guidance on location data risk in OOH points to the same conclusion: vetting and contracts carry the weight that a website’s cookie banner would carry online.
- Require consent-chain records showing where and how location data was originally collected.
- Confirm the vendor excludes sensitive-location categories from any location product sold to you.
- Get written retention and deletion policies, plus a current subprocessor list.
- Demand contractual clauses covering lawful-collection representations, audit rights, deletion obligations, and incident reporting timelines.
Pro Tip: Ask for a sample data slice before signing anything. A vendor confident in its consent chain will usually let you inspect a redacted sample; one that hesitates is telling you something.
Where available, request SOC 2 or ISO attestations and, for higher-risk vendors, the right to review their own data protection assessments rather than taking a one-line assurance at face value.
Privacy-preserving measurement and first-party alternatives
You do not need identifiable location data to prove an OOH campaign worked. Differential privacy, federated learning, and aggregated threshold reporting let vendors share directional insight without exposing individual device trails, an approach industry guidance increasingly recommends as OOH adopts AdTech-style attribution.
- QR-code opt-in flows give you consented, first-party attribution tied to a specific campaign asset.
- Campaign landing pages and loyalty program integrations generate measurement data you collected directly, not through a reseller.
- Gated offers redeemed in-store or online create a consented conversion signal without device-level tracking.
- Panel-based uplift studies and modeled attribution work well when you need directional lift without individual-level data at all.
Our guide to smart data collection in OOH walks through how to set up first-party capture without leaning on third-party location brokers.
Consent, opt-outs, and consumer-facing execution for OOH
A billboard cannot ask for consent, but everything connected to it, from a QR code to a retargeting pixel, can. Route the physical exposure toward a digital moment where consent is explicit and recorded.
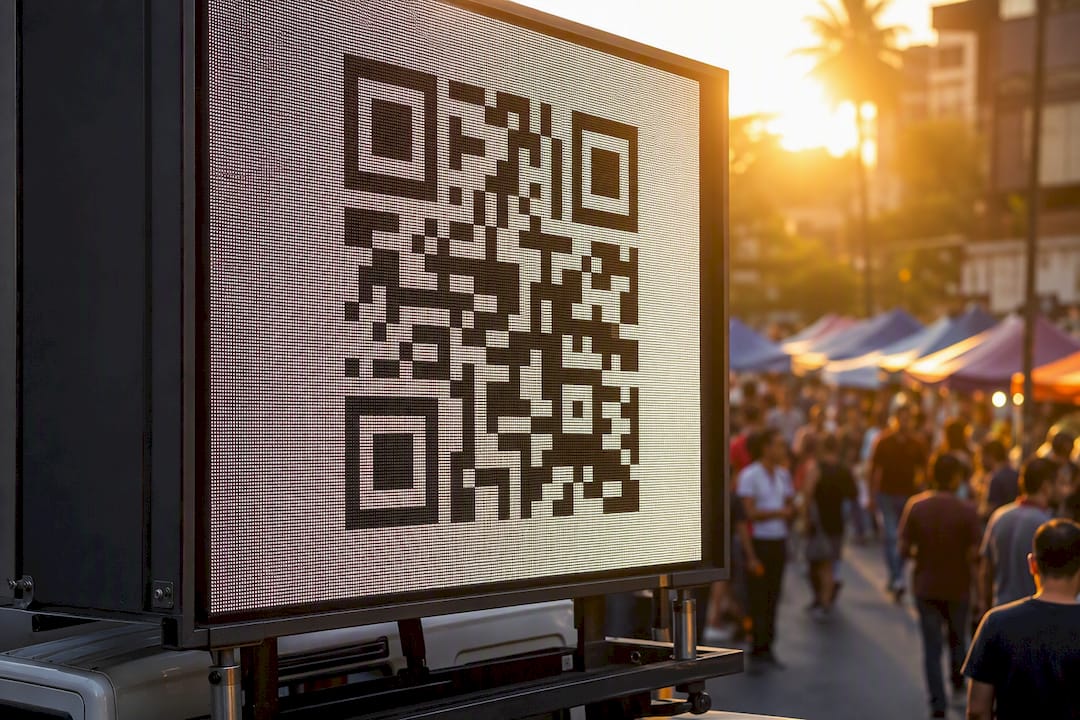
- Link QR codes to a short landing page with a clear consent choice before any data capture happens.
- Use in-app or SMS confirmation flows for any data collected through a rideshare wrap scan or mobile activation.
- Honor browser and platform opt-out signals, plus state-specific tools like California’s DROP deletion platform, which centralizes deletion requests to registered data brokers.
- Publish a privacy notice with plain-language purpose statements and two designated request methods, typically a webpage form plus an email or phone line.
Pro Tip: Test your own QR flow as a consumer would. If you cannot find the consent screen within two taps, neither can your campaign’s audience.
A related practical check for CCPA-specific testing appears in this opt-out validation guide, which walks through the checks advertisers should run before a campaign goes live.
Recordkeeping and incident response for OOH campaigns
Enforcement actions consistently reward companies that can produce records quickly and penalize ones that cannot reconstruct what happened. Build the habit of keeping a defined set of documents for every campaign.
- Retain supplier assessments, data protection assessments, consent logs, retention schedules, and measurement records for the full campaign lifecycle plus a defined retention period after it ends.
- If an incident occurs, contain it immediately, notify the responsible vendor in writing, and determine whether consumer or regulator notification is required under the applicable state law.
- Assemble these records into a single campaign privacy folder so you can respond to an audit or inquiry without scrambling to find scattered emails and vendor contracts.
This folder becomes your primary evidence of good faith if a regulator or a client’s legal team ever asks how a campaign handled location or attribution data.
How Beacon Mobile Media maps OOH execution to privacy controls
Beacon Mobile Media runs LED mobile billboards and wrapped rideshare vehicles with geofencing and route customization, which limits targeting to defined areas instead of individual devices. Smart QR codes capture data through consumer scans, and proof-of-posting with GPS and photo tracking gives campaigns a documented record for compliance review. This is illustrative of how OOH execution can support a compliance checklist, not a substitute for legal advice.
Data retention and deletion policies specific to OOH data
OOH campaigns generate several distinct categories of data: QR-code scan records, geofence entry and exit logs, attribution reports tying exposure to conversions, and any consumer contact information collected through a landing page. Each category needs its own retention rule rather than a single blanket policy.
Scan and geofence data tied to an individual device should have the shortest retention window, since it carries the highest re-identification risk. Once a campaign’s attribution window closes, typically 30 to 90 days depending on the sales cycle you are measuring, device-level records should be deleted or aggregated into reporting that no longer ties back to an individual.

Aggregated performance reports, the kind you share internally or with a client, can be retained longer because they no longer carry the same privacy exposure, provided the underlying raw data has already been deleted or anonymized on schedule.
Build deletion into the contract with every vendor before a campaign starts, not after a complaint arrives. The FTC’s Kochava settlement specifically requires a deletion schedule as part of its remedy, which signals that “we’ll delete it eventually” is no longer an acceptable retention policy for location-adjacent data. Put the schedule in writing: what gets deleted, on what timeline, and who confirms it happened.
Employee training and internal compliance programs for OOH privacy
A written privacy policy does nothing if the media buyer signing a data deal does not know what a sensitive-location exclusion is supposed to look like. Internal training should cover a few specific, practical points rather than a general privacy overview.
Media buyers and campaign managers need to know how to recognize a location dataset that carries elevated risk, what questions to ask a vendor before signing, and who internally approves a new data source. Creative and operations teams need to understand why a QR-code consent screen cannot be skipped for the sake of a faster scan-to-landing-page experience.
Assign a single internal point of contact, even in a small marketing team, responsible for reviewing new vendor contracts against your supplier assessment checklist. That person does not need a legal title, but they do need the authority to pause a campaign if a vendor cannot answer basic consent-chain questions.
Build a short annual refresher tied to any law changes, since state privacy rules are still evolving quickly. A training program that existed once at onboarding and never again will not hold up well if a regulator asks how your team stays current.

Handling consumer data subject access requests (DSARs) in OOH context
A consumer who scanned a QR code at an OOH activation, or whose device appeared in a geofence report, has the same access and deletion rights under state law as someone who filled out a web form. The challenge in OOH is that the data often sits with a third-party vendor rather than your own systems.
Set up a defined process before you need it. When a DSAR arrives, you need to know within hours which vendors might hold data tied to that person, how to request deletion or an access report from them, and how to confirm the request was fulfilled.
Your privacy notice should list two designated methods for consumers to submit a request, typically a webpage form and an email or phone contact, consistent with California’s disclosure requirements. Build the vendor contact list into your supplier assessment records so a request does not require tracking down a forgotten point of contact from a campaign that ran months earlier.
Respond within the timeline your state’s law requires, and keep a log of each request and its resolution. That log becomes part of the same privacy folder you maintain for audits and incident response.
International privacy regulations affecting OOH campaigns
Most OOH campaigns run entirely within U.S. markets, so U.S. federal and state law is the primary framework that applies. If a campaign or its data processing touches the European Union, such as a vendor’s analytics platform hosted abroad or a client running parallel campaigns internationally, GDPR’s consent and data-minimization principles become relevant for that portion of the data flow.
The safest practical approach is to treat any cross-border data transfer as a separate compliance question with its own vendor assessment, rather than assuming a U.S.-focused privacy notice covers it. If your OOH program has no international data flows, GDPR simply does not apply, and the state laws already covered in this guide remain your governing framework.
For any brand running OOH alongside international digital campaigns, aligning your location-data policies across channels avoids a situation where your digital team follows a stricter standard than your outdoor team does for comparable data.
What this means for OOH teams right now
Regulators are drawing a hard line around precise-location data faster than most OOH contracts have caught up. Waiting for a settlement to name your vendor is not a plan. Build the supplier checklist and prefer first-party, consented data now.
— Scott
Beacon Mobile Media: privacy-conscious OOH execution
Running a compliant OOH campaign takes less effort when your vendor already builds route-level targeting, QR-code consent capture, and proof-of-posting into the campaign from day one. This vendor pairs LED mobile billboards and wrapped rideshare vehicles with documented, consent-based data capture instead of unverified third-party location purchases.

- Route customization and geofencing target defined areas.
- Smart QR codes capture consumer data through opt-in scans.
- Proof-of-posting with GPS and photo tracking provide documented records for placements.
- Attribution reporting ties campaign exposure to results without relying solely on unverified location data brokers.
Request a campaign consult through Beacon-ads to see how route-level targeting and consented data capture can fit your next OOH campaign.
Sources
- FTC to Ban Kochava and Subsidiary from Selling Sensitive Location Data to Settle Charges They Sold Location Data Linked to Millions of Mobile Devices
- California Consumer Privacy Act of 2018
- Colorado Privacy Act (CPA) – Colorado Attorney General
FAQ
What is OOH privacy compliance?
OOH privacy compliance means handling any data collected through out-of-home advertising, such as QR-code scans or geofence-based targeting, in line with federal enforcement standards and state privacy laws. It centers on verifying consent for location data, limiting collection near sensitive locations, and documenting vendor practices rather than relying on a single generic privacy policy.
Does GDPR apply to OOH campaigns in the United States?
GDPR generally does not apply to OOH campaigns that run entirely within the United States and use U.S.-based vendors. It becomes relevant only if a campaign’s data processing crosses into the European Union, such as through an international vendor or a parallel EU campaign, in which case that specific data flow should be assessed separately.
What counts as precise geolocation under California law?
California’s CCPA statute defines precise geolocation as location data accurate enough to identify a specific point within a defined radius. Data at this level tied to a device identifier is treated as sensitive and carries stricter disclosure and opt-out obligations than general location data.
How do I handle a data deletion request tied to an OOH campaign?
Identify which vendors might hold data tied to the requester, such as a QR-code scan or geofence log, and request deletion or an access report from each one. Respond within your state’s required timeline and log the request and resolution in your campaign’s compliance records.
What should a vendor assessment checklist include for OOH data suppliers?
A solid assessment checks for verifiable consent-chain records, exclusion of sensitive-location categories, written retention and deletion schedules, and an up-to-date subprocessor list. It should also confirm contractual rights to audit the vendor and review incident reporting timelines, consistent with the requirements set out in the FTC’s Kochava settlement.